-
Chicago: 312-554-7550
-
St. Louis : 314-432-1661
-
Metro East IL : 618-346-8324
-
Central IL : 217-528-0500
Google Warns AI Is Dramatically Speeding Up Cyberattacks
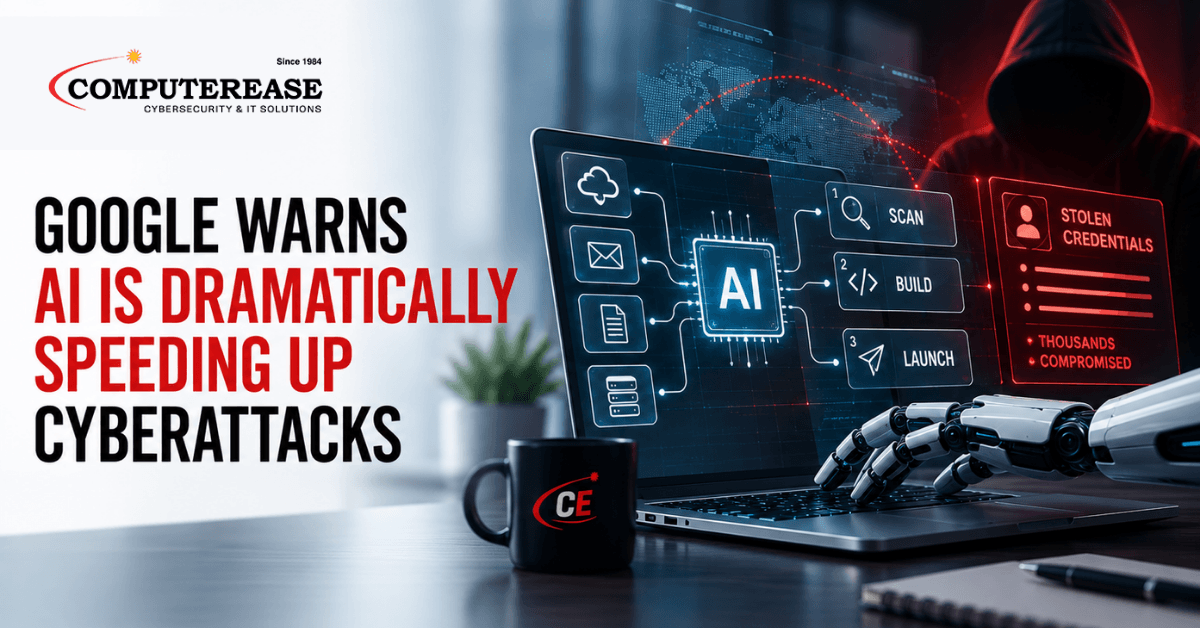
A financially motivated attacker used an AI coding chatbot, a prompt, and a set of agent instructions to plan, build, and launch a mass credential-harvesting campaign.
Start to finish, it took less than six hours.
That’s one of the examples in a new report from Google’s Threat Intelligence Group (GTIG), and it’s worth paying attention to. Google says attackers are moving beyond simply asking AI for help and beginning to use AI-powered systems that can automate multiple stages of an attack with far less human involvement.
This isn’t a story about one new piece of malware or a single vulnerability. It’s about how AI can help attackers move faster and operate at a scale that once required considerably more people and resources.
What Google’s Report Actually Found
According to GTIG, both cybercriminals and state-sponsored groups are increasingly using AI to automate and accelerate different parts of their operations.
One of the clearest examples involved a suspected financially motivated attacker that had already compromised an organization’s cloud infrastructure. The attacker used an AI coding chatbot, a prompt, and a set of agent instructions to plan, build, and execute a mass credential-harvesting campaign in less than six hours. The AI-powered framework handled tasks including vulnerability scanning, troubleshooting, credential harvesting, and IP rotation with far less manual intervention. Google says the operation compromised thousands of third-party credentials.
That speed and automation are the point. Google says these newer agentic workflows dramatically reduce the amount of human involvement required, compressing the traditional window defenders have to respond.
Google’s report describes another financially motivated group, UNC6780, also known as TeamPCP, that illustrates a different AI-related risk. Since March 2026, the group has conducted large-scale open-source software supply-chain compromises involving ecosystems including PyPI, npm, and Docker Hub. Google says the group has used multiple methods to target AI coding assistants, development tools, and open-source software practices.
The report also documents state-sponsored groups using AI across multiple stages of their operations, including researching targets, drafting and translating social-engineering messages, developing malware, and troubleshooting post-exploitation activity.
Why AI Lowers the Barrier for Attackers
The important part of Google’s report isn’t simply that sophisticated state-sponsored groups are using AI. It’s that AI can also give financially motivated attackers more automation and speed without requiring the same amount of manual work.
Tasks such as reconnaissance, vulnerability research, phishing-lure development, coding, troubleshooting, and credential harvesting can increasingly be assisted or automated by AI. That doesn’t turn an inexperienced criminal into an elite hacker with a single prompt. It does mean a capable attacker may be able to accomplish more work with fewer people and in less time.
For small and mid-sized businesses, that’s an important shift. Attackers don’t necessarily need to invest the same amount of time in every potential victim when more of the work can be automated.
Why This Matters for Small and Mid-Sized Businesses
The six-hour example shows how quickly an AI-assisted operation can move once an attacker already has the infrastructure and access needed to get started. In this case, Google says the attacker had first compromised an organization’s cloud infrastructure and then used it to help carry out the credential-harvesting operation.
For businesses, the larger lesson isn’t that every cyberattack will now happen in six hours. It’s that AI can help attackers automate work that previously required more time and manual effort, putting more pressure on businesses to detect suspicious activity quickly.
The report also reinforces why open-source software supply-chain risk deserves attention. If your development team, or a software vendor you rely on, uses packages from repositories such as PyPI, npm, or Docker Hub, the open-source supply-chain activity Google documented is worth paying attention to.
What a Business Can Actually Do About This
Treat Microsoft 365 account protection as a top priority, not a background task. Enforce multi-factor authentication, use unique passwords, and monitor for suspicious sign-ins, unusual mailbox rules, and other signs that an account may have been compromised.
Assume faster detection matters more than ever. Google’s findings show how automation can compress parts of the attack lifecycle. Monitoring and response need to keep pace rather than depending entirely on periodic manual review.
Ask vendors and developers about their open-source dependency review. If your business relies on custom software or a development partner, ask how they review and monitor the packages they pull into your applications rather than simply assuming those packages are safe.
Don’t assume small size makes you uninteresting to an attacker. When scanning, reconnaissance, credential harvesting, and other parts of an attack can be automated, criminals can operate across more potential targets with less manual effort.
Include AI tools in your normal security reviews. Google’s report also describes attackers targeting AI credentials, models, source code, and cloud resources. As businesses adopt more AI tools, those systems and accounts need to be treated like other business technology: know who has access, what information they can reach, and who is responsible for securing them.
Is Your Business Ready for Faster, AI-Assisted Threats?
Attackers are finding new ways to use AI to automate work that once took considerably more time and effort. That makes the security basics businesses already depend on—protected accounts, updated systems, monitoring, backups, and a clear response plan—even more important.
Our Free Cybersecurity & AI Risk Assessment can help identify gaps in your current security environment and give you a clearer picture of what deserves attention first.
Complete This Form To Claim Your FREE Cyber Security & AI Risk Assessment
Frequently Asked Questions
No. Google’s report does not say small businesses are suddenly being targeted by nation-state hackers. The important takeaway is that AI can help financially motivated criminals automate more of their work and operate with greater speed and scale. That makes strong security fundamentals important regardless of company size.
Credential harvesting is the practice of collecting usernames, passwords, and login details, often through phishing, fake login pages, or exploiting exposed systems, to gain unauthorized access to accounts and systems.
It’s related, but different. Earlier concerns about agentic AI focused on what can happen when AI systems are given the ability to take actions inside real environments. Google’s new report shows attackers using those same kinds of autonomous capabilities offensively, allowing AI-powered systems to handle tasks such as scanning, troubleshooting, and credential harvesting with less human intervention.
Traditional security tools still matter. The change is that faster, more automated attacks put greater pressure on monitoring and response. Organizations that depend heavily on periodic manual review may have less time to recognize and contain suspicious activity.
Start with the basics attackers repeatedly try to exploit: protect accounts with MFA, keep internet-facing systems patched, monitor Microsoft 365 and other critical accounts for suspicious activity, and make sure someone is responsible for responding when an alert appears. If your business develops software, review how open-source packages and dependencies are approved and monitored.
Key Takeaways
- Google’s Threat Intelligence Group documented a financially motivated attacker using an AI coding chatbot and agent instructions to plan, build, and execute a mass credential-harvesting campaign in less than six hours. The operation compromised thousands of third-party credentials.
- Google is seeing both cybercriminals and state-sponsored groups use AI across more stages of the attack lifecycle, from reconnaissance and social engineering to malware development and troubleshooting.
- Separately, UNC6780, also known as TeamPCP, has targeted open-source ecosystems including PyPI, npm, and Docker Hub as part of large-scale software supply-chain compromises since March 2026.
- The larger concern for businesses is speed and automation: AI can allow attackers to complete more work with less manual intervention.
Strong account security, monitoring, patching, response capabilities, and software supply-chain controls become more important as attackers automate more of their work.
Source: Google Threat Intelligence Group, “GTIG AI Threat Tracker: From Prompting to Autonomy: The Evolution of Adversarial AI,” September 8, 2026.